How to See Who Ran a Script on a Client's Server: Audit Trail
Breeze RMM records every action taken through it in an append-only, hash-chained audit trail, so you can answer "who touched our server on Tuesday?" with records, then use the server's own event log to show what actually broke.
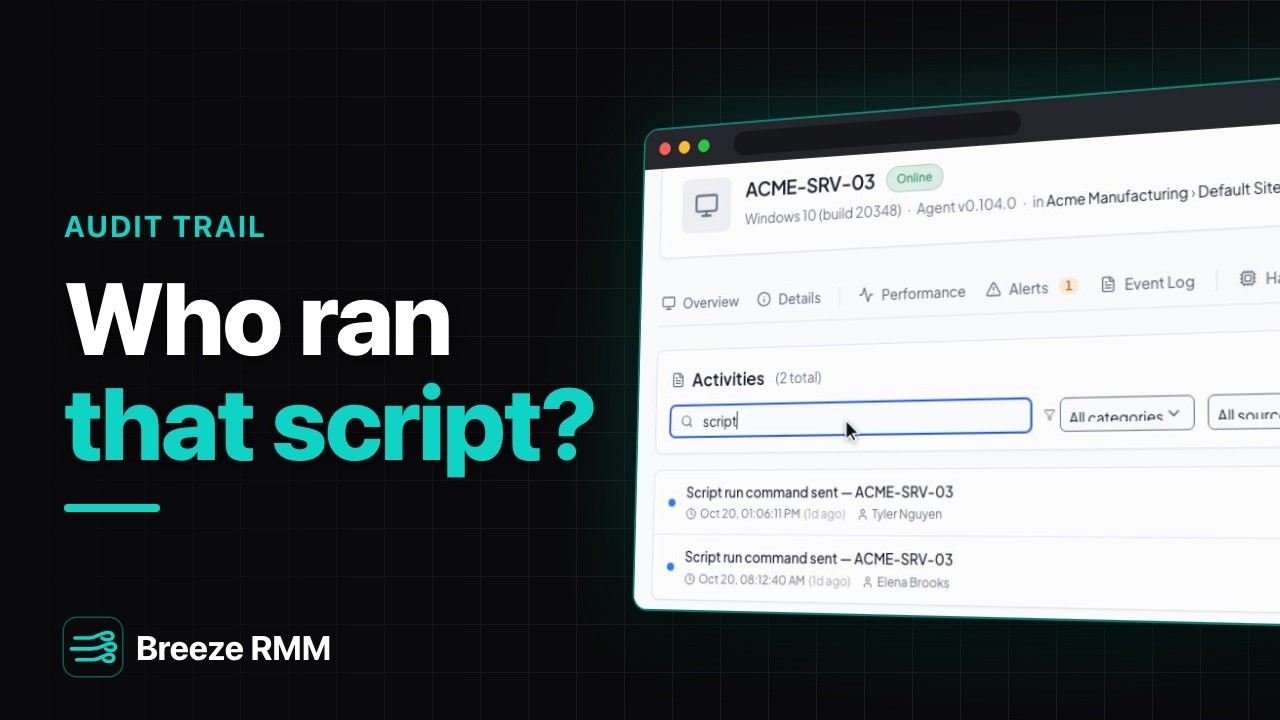
3:56 Captions: English Open on YouTube
What's in the demo
- Reporting → Audit Trail with Acme Manufacturing selected: each row shows who, when, the action, the resource and the IP address
- ACME-SRV-03 → Activities, searched for "script": two "Script run command sent" entries for ACME-SRV-03 on Oct 20, Tyler Nguyen at 1:06 PM and Elena Brooks at 8:12 AM
- Tyler's entry expanded: action agent.command.script, his name, the time, and in the details the script's length and SHA-256 fingerprint ("redacted": true) instead of the script body
- Audit Trail → Filters → User: Tyler Nguyen. His request reads Script execute, Restart Print Spooler, 203.0.113.24; expanded, a manual run as system from Chrome
- Export Logs: audit-logs-2026-10-22.csv, 1 row, 14 columns, exactly what the filter shows
- ACME-SRV-03 → Event Log at level Error: three spoolsv.exe crashes in LabelPro64.dll and "The Print Spooler service terminated unexpectedly. It has done this 3 time(s)."
- Level back to all levels: on Monday night the LabelPro Print Driver was installed from C:\Users\Administrator\Downloads, outside Breeze
- Acme's organization settings → Audit Retention: 365 days
- Organization settings → Event Logs → Log Forwarding: "Enable log forwarding" ticked, endpoint https://logs.acmemfg.example:9200, index prefix acme-logs, API key authentication
Questions this video answers
- How do I see who ran a script on a client's server in Breeze RMM?
- Open the device, go to its Activities tab (the audit trail for that one device) and search "script". Each run shows as "Script run command sent" with the technician and the time. Then in Reporting → Audit Trail, filter by that technician to see the request itself, with the script name and IP address.
- Does the audit log store the script that ran?
- No. It stores the script's length and a SHA-256 fingerprint of the exact body, plus how it ran (manual, as system), so you can prove which version ran without copying the script into the log.
- Can audit log entries be edited or deleted?
- Not from Breeze, not even by an admin. The trail is append-only, each entry is chained to the one before it by a hash, and Breeze re-checks the chain every day. How long entries are kept is set per client under Audit Retention (default 365 days).
- Can I export the audit trail?
- Yes. Export Logs downloads the filtered view as a CSV with every column, details included, and the export itself is written to the audit trail.
- Can Breeze forward event logs to a SIEM?
- Yes, to an Elasticsearch- or OpenSearch-compatible endpoint with an API key or username and password, set per client under organization settings → Event Logs, or once for every client at the partner level. Logs ship as agents send them, into a new index each day.
A note on the demo: all people, devices, IP addresses and the LabelPro driver are fictional demo data. Log forwarding is filled in but not saved, and the endpoint is a placeholder.
Do this on your own fleet
Everything in the video is in the product you get. Start the Cloud Beta in minutes, or self-host the open-source Community edition for free.