The Workers
The workers: Breeze's built-in AI that acts safely across your fleet.

Chapters and notes → Also: How to Track, Cap and Bill Back AI Costs per Client (3:42)Also: How to Let AI Remediate a CVE, With Your Approval (2:35)Also: How to Set Up AI Agents That Propose Fixes and Wait for Approval (4:09)Also: How to Approve AI Actions Before They Run: the Approvals Queue (3:24) All videos
Breeze ships with the workers: built-in AI that can investigate device issues, query fleet state, and execute actions through the same controls your team uses. Every mutating call is governed by the AI Risk Engine, so nothing touches a device without policy and approval checks behind it. In the product, the workers live under Settings → AI Brain. The workers are the core of what makes Breeze an AI RMM: governed AI doing the operations, not a chatbot bolted onto a dashboard.
AI Risk Engine
The Risk Engine classifies every AI operation into one of four tiers:
- Tier 1: Read-only operations that auto-execute.
- Tier 2: Low-risk mutating actions that auto-execute and audit log.
- Tier 3: Higher-risk actions that require explicit human approval.
- Tier 4: Blocked actions that never execute.
Tier assignment is action-level and context-aware. The same tool can run at different tiers depending on intent, scope, and timing. A reboot inside a maintenance window is Tier 2, but the same call outside one escalates to Tier 3.
Approvals, rejections, rate-limit state, and security events all surface in the Risk Engine dashboard. See AI Risk Engine for the full model.
Fleet-Oriented AI Operations
From the Fleet view, the AI can orchestrate cross-fleet workflows for policies, deployments, patches, groups, automations, alert rules, and reports. The same tooling handles one-device triage and large-scale maintenance, useful for both daily help-desk work and quarterly remediation pushes.
Device context memory keeps known issues, quirks, follow-ups, and preferences scoped to each organization, so the workers don’t lose state between conversations.
Connecting External AI Clients
External AI clients (Claude.ai, ChatGPT, Cursor, Windsurf) connect to Breeze through a full OAuth 2.1 stack with Dynamic Client Registration and PKCE. Clients self-register on first connect, the user approves scopes through a standard authorization screen, and the client receives short-lived access tokens with rotating refresh. Revoking a grant invalidates every sibling token immediately, with no waiting for expiry.
The MCP endpoint speaks both SSE and the newer Streamable HTTP transport defined in the latest MCP specification, so modern OAuth-capable clients and legacy SSE clients work side by side. Pasted API keys remain an option for self-hosters who prefer them; audit logging is identical on both paths.
Deeper details live in Authentication and MCP Server.
The Workers, and Wisp
The workers (included free) handle single-event reactive triage: they receive an event, investigate with the tool catalog, and recommend or execute inside the risk engine. They wait to be asked or triggered. You bring your own Anthropic API key and supervise them yourself.
Wisp is hosted on Breeze Cloud and comes to you: one Wisp per operator that watches their customers continuously, nudges them with one subject and one next step, asks before anything consequential, remembers what it is told, hands bounded work to the specialist agents, and never acts above the authority of the human it works for. It is priced per person, with every price on the pricing page.
The RMM Is Always the Final Authority
Whether a human technician, the workers or Wisp is doing the work, every action passes through the same gate: the Breeze Risk Engine validates it locally against your risk classifications, maintenance windows, and approval policies. The AI can request actions; your Breeze instance decides whether to allow them.
Tenant Isolation and Rate Limits
Every AI call carries the tenant context of the caller, and tenant boundaries are enforced down to the database with row-level security. An AI client connected for one customer cannot see or touch another, regardless of which tool is called.
AI tool calls and MCP connections are rate-limited per organization, with state visible in the Risk Engine dashboard. Exceeding a limit returns a throttle response with retry timing instead of silently dropping requests, so misbehaving clients fail loudly and stay observable.
Tool Catalog
The workers expose the same tool groups across self-run and managed modes:
- Device tools: list devices, get details, query fleet state.
- Alert tools: retrieve alerts, update status, link to tickets.
- Action tools: reboot, shutdown, lock, isolate, install, uninstall.
- Patch tools: patch status and scheduled deployments.
- Script tools: execute PowerShell, Bash, or Python with result retrieval.
- Report tools: compliance, security, inventory, and executive reports.
- Documentation tools: runbooks, incident notes, change logs.
Every tool inherits a tier classification, and the same tool can resolve to different tiers depending on context.
Optional Browser Telemetry
Self-hosters can opt in to browser-side error tracking and on-error session replay by providing a Sentry DSN. When enabled, text, inputs, URLs, IDs, cookies, headers, and request bodies are aggressively masked before anything leaves the browser. Telemetry stays off by default; nothing is collected unless you explicitly turn it on. See Error Tracking for the full configuration model.
Learn More
- Let an AI client set up Breeze: provision a complete Breeze tenant over MCP, no web UI required.
- AI Risk Engine: tier definitions, approval workflow, and rate-limit visibility.
- MCP Server: how external AI clients connect to the same toolset.
- Authentication: OAuth 2.1, scoped keys, and identity across humans and AI clients.
- What Breeze AI Can Do For Your Help Desk: practical triage and remediation walkthroughs.
Interactive demo · click through it yourself
5 steps
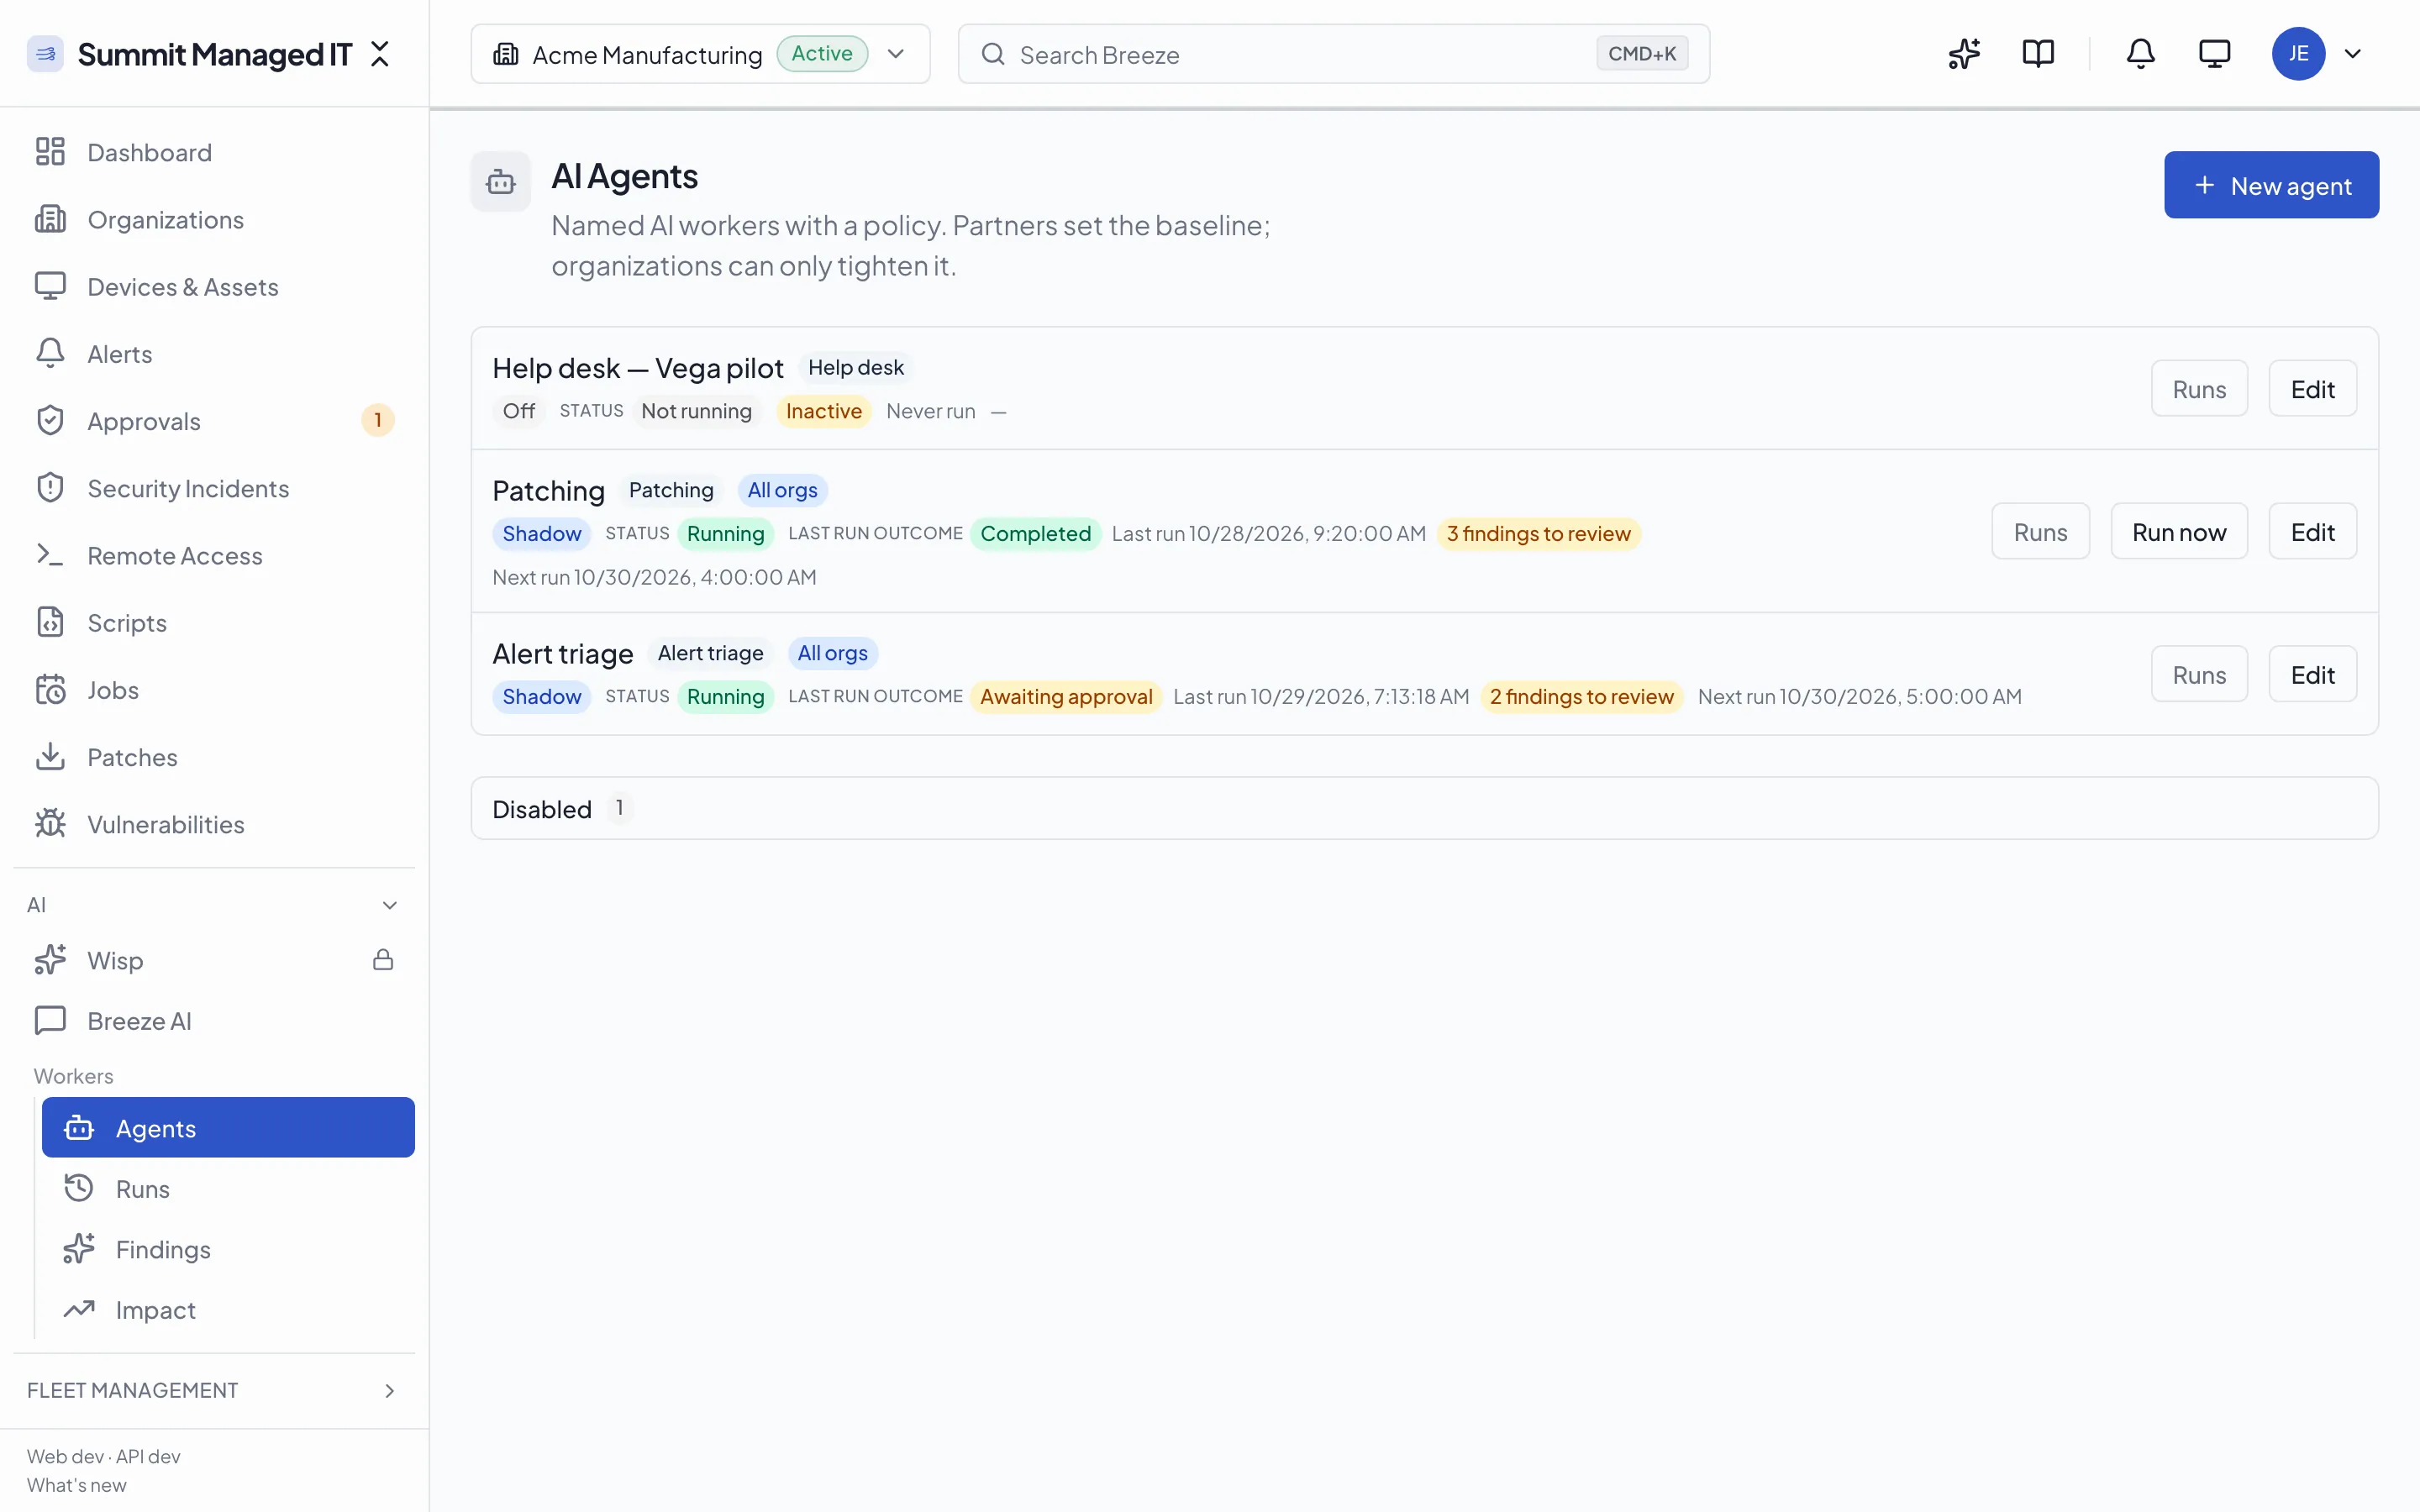
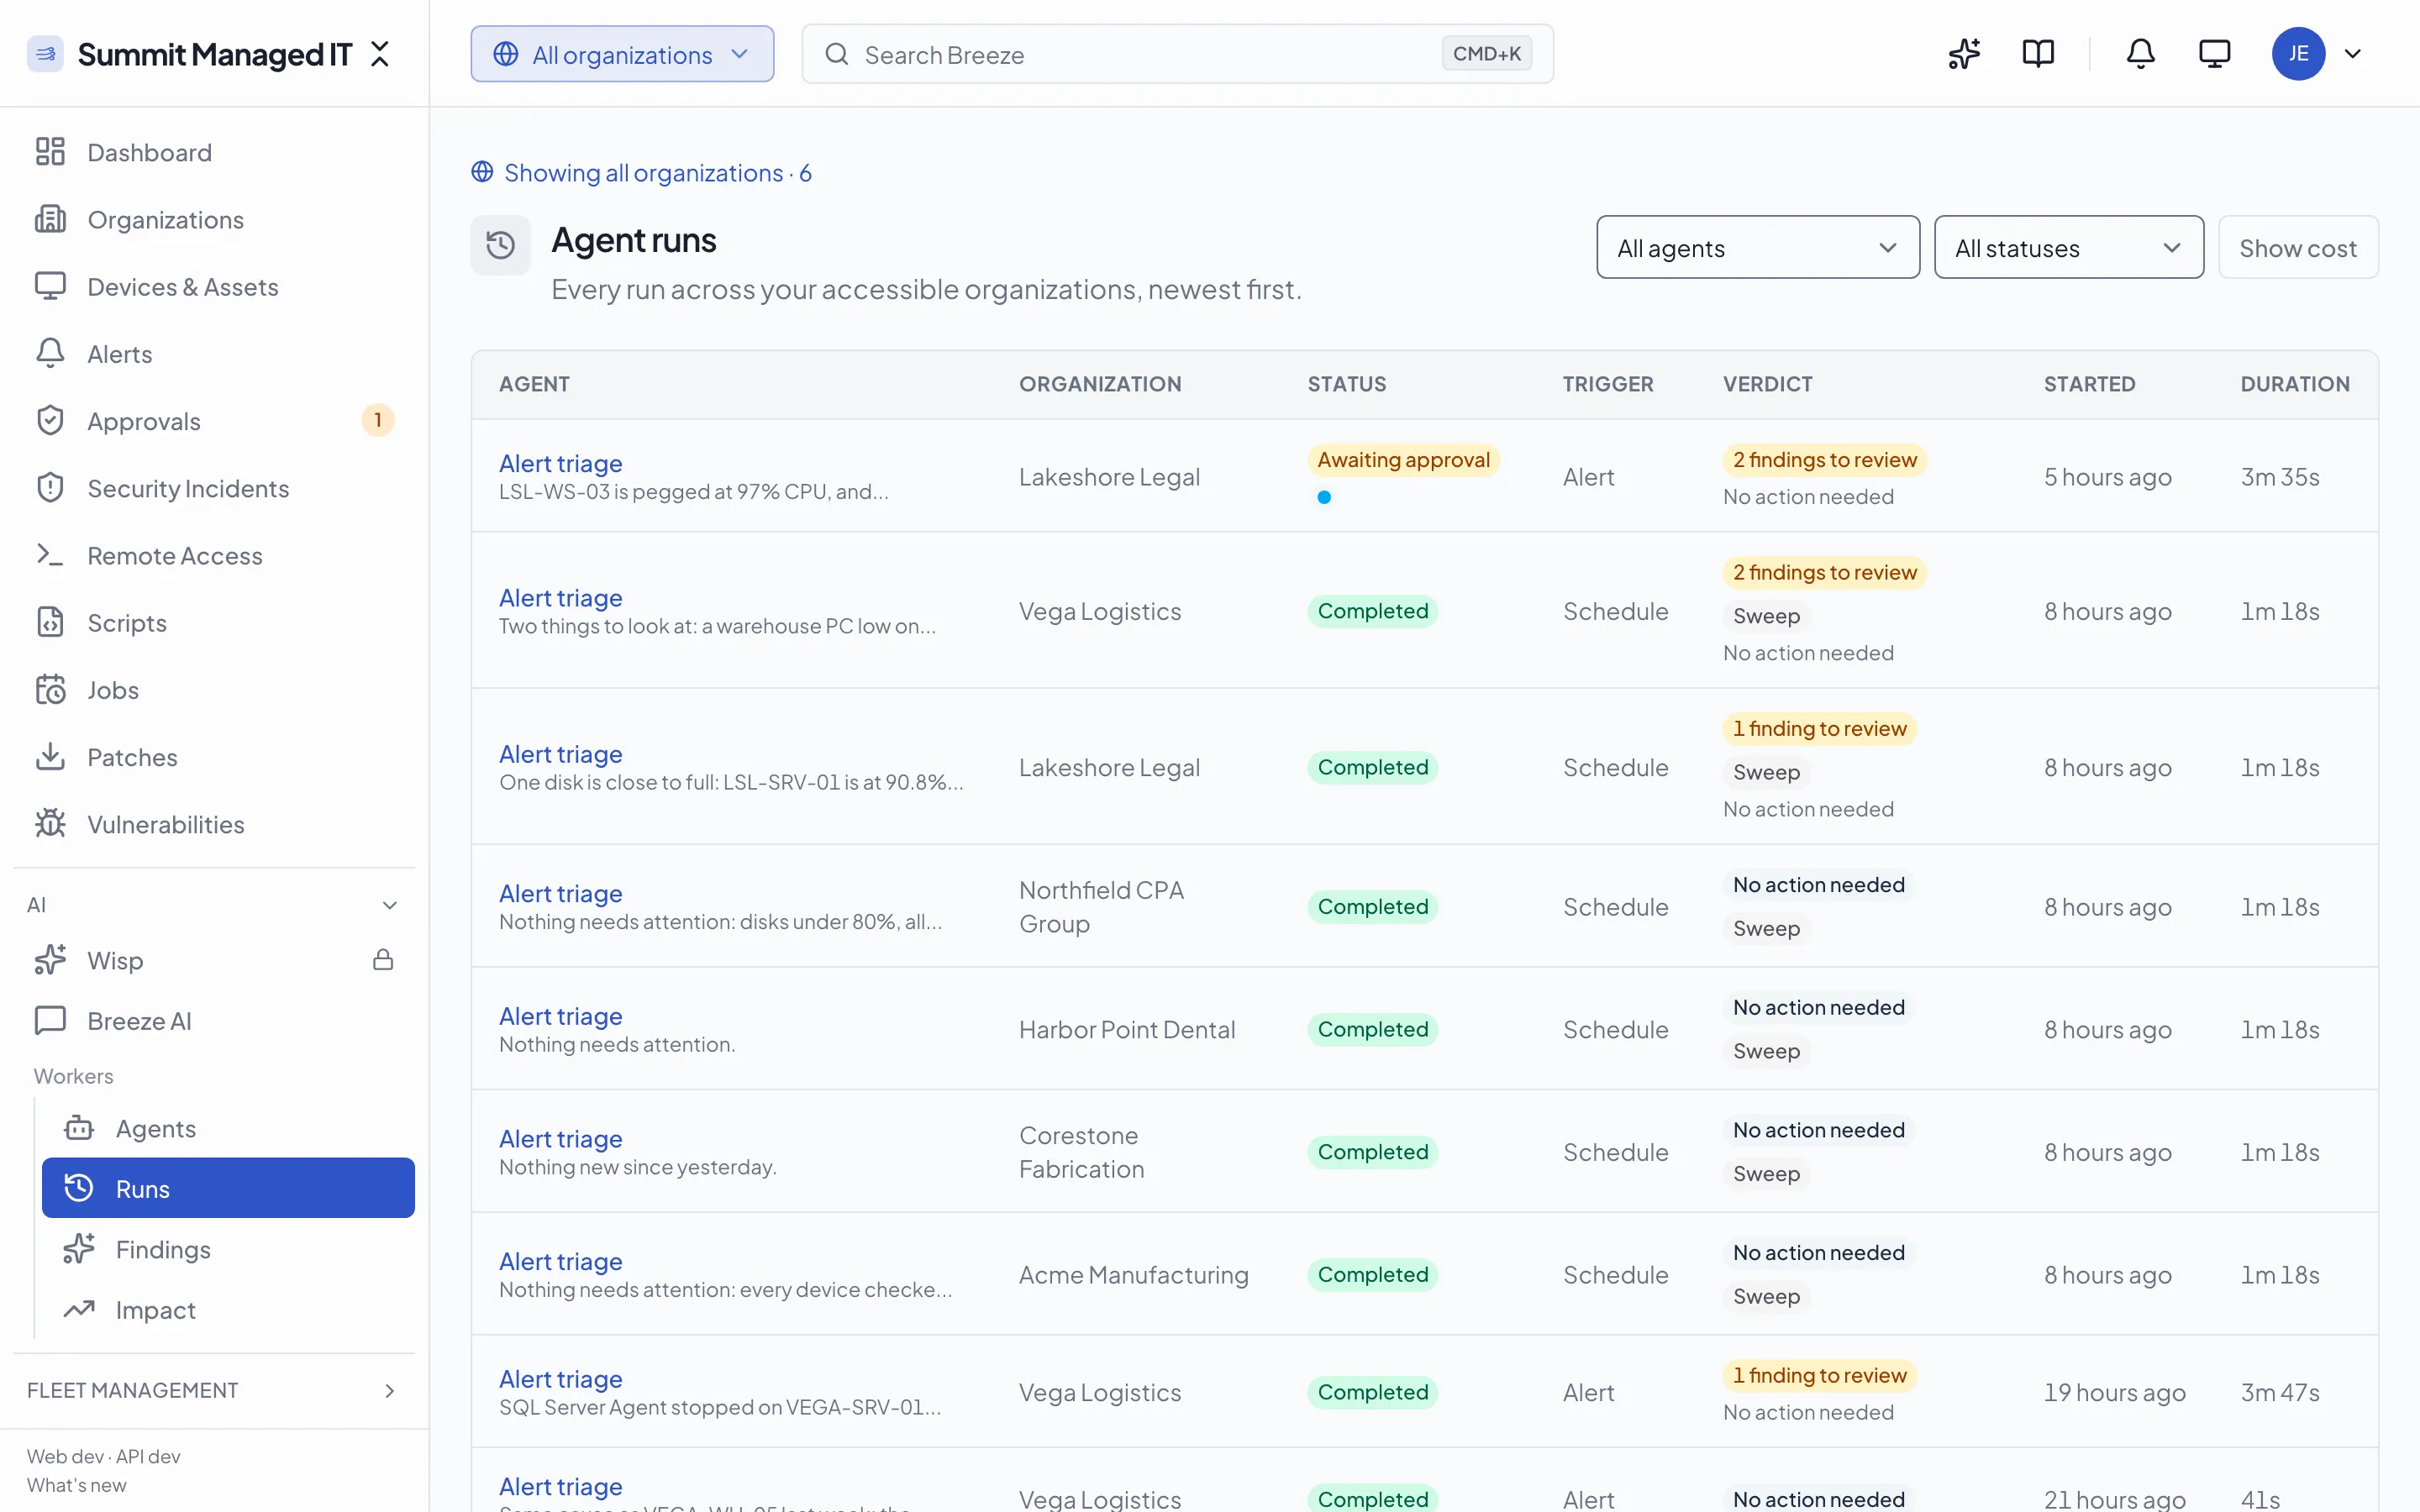
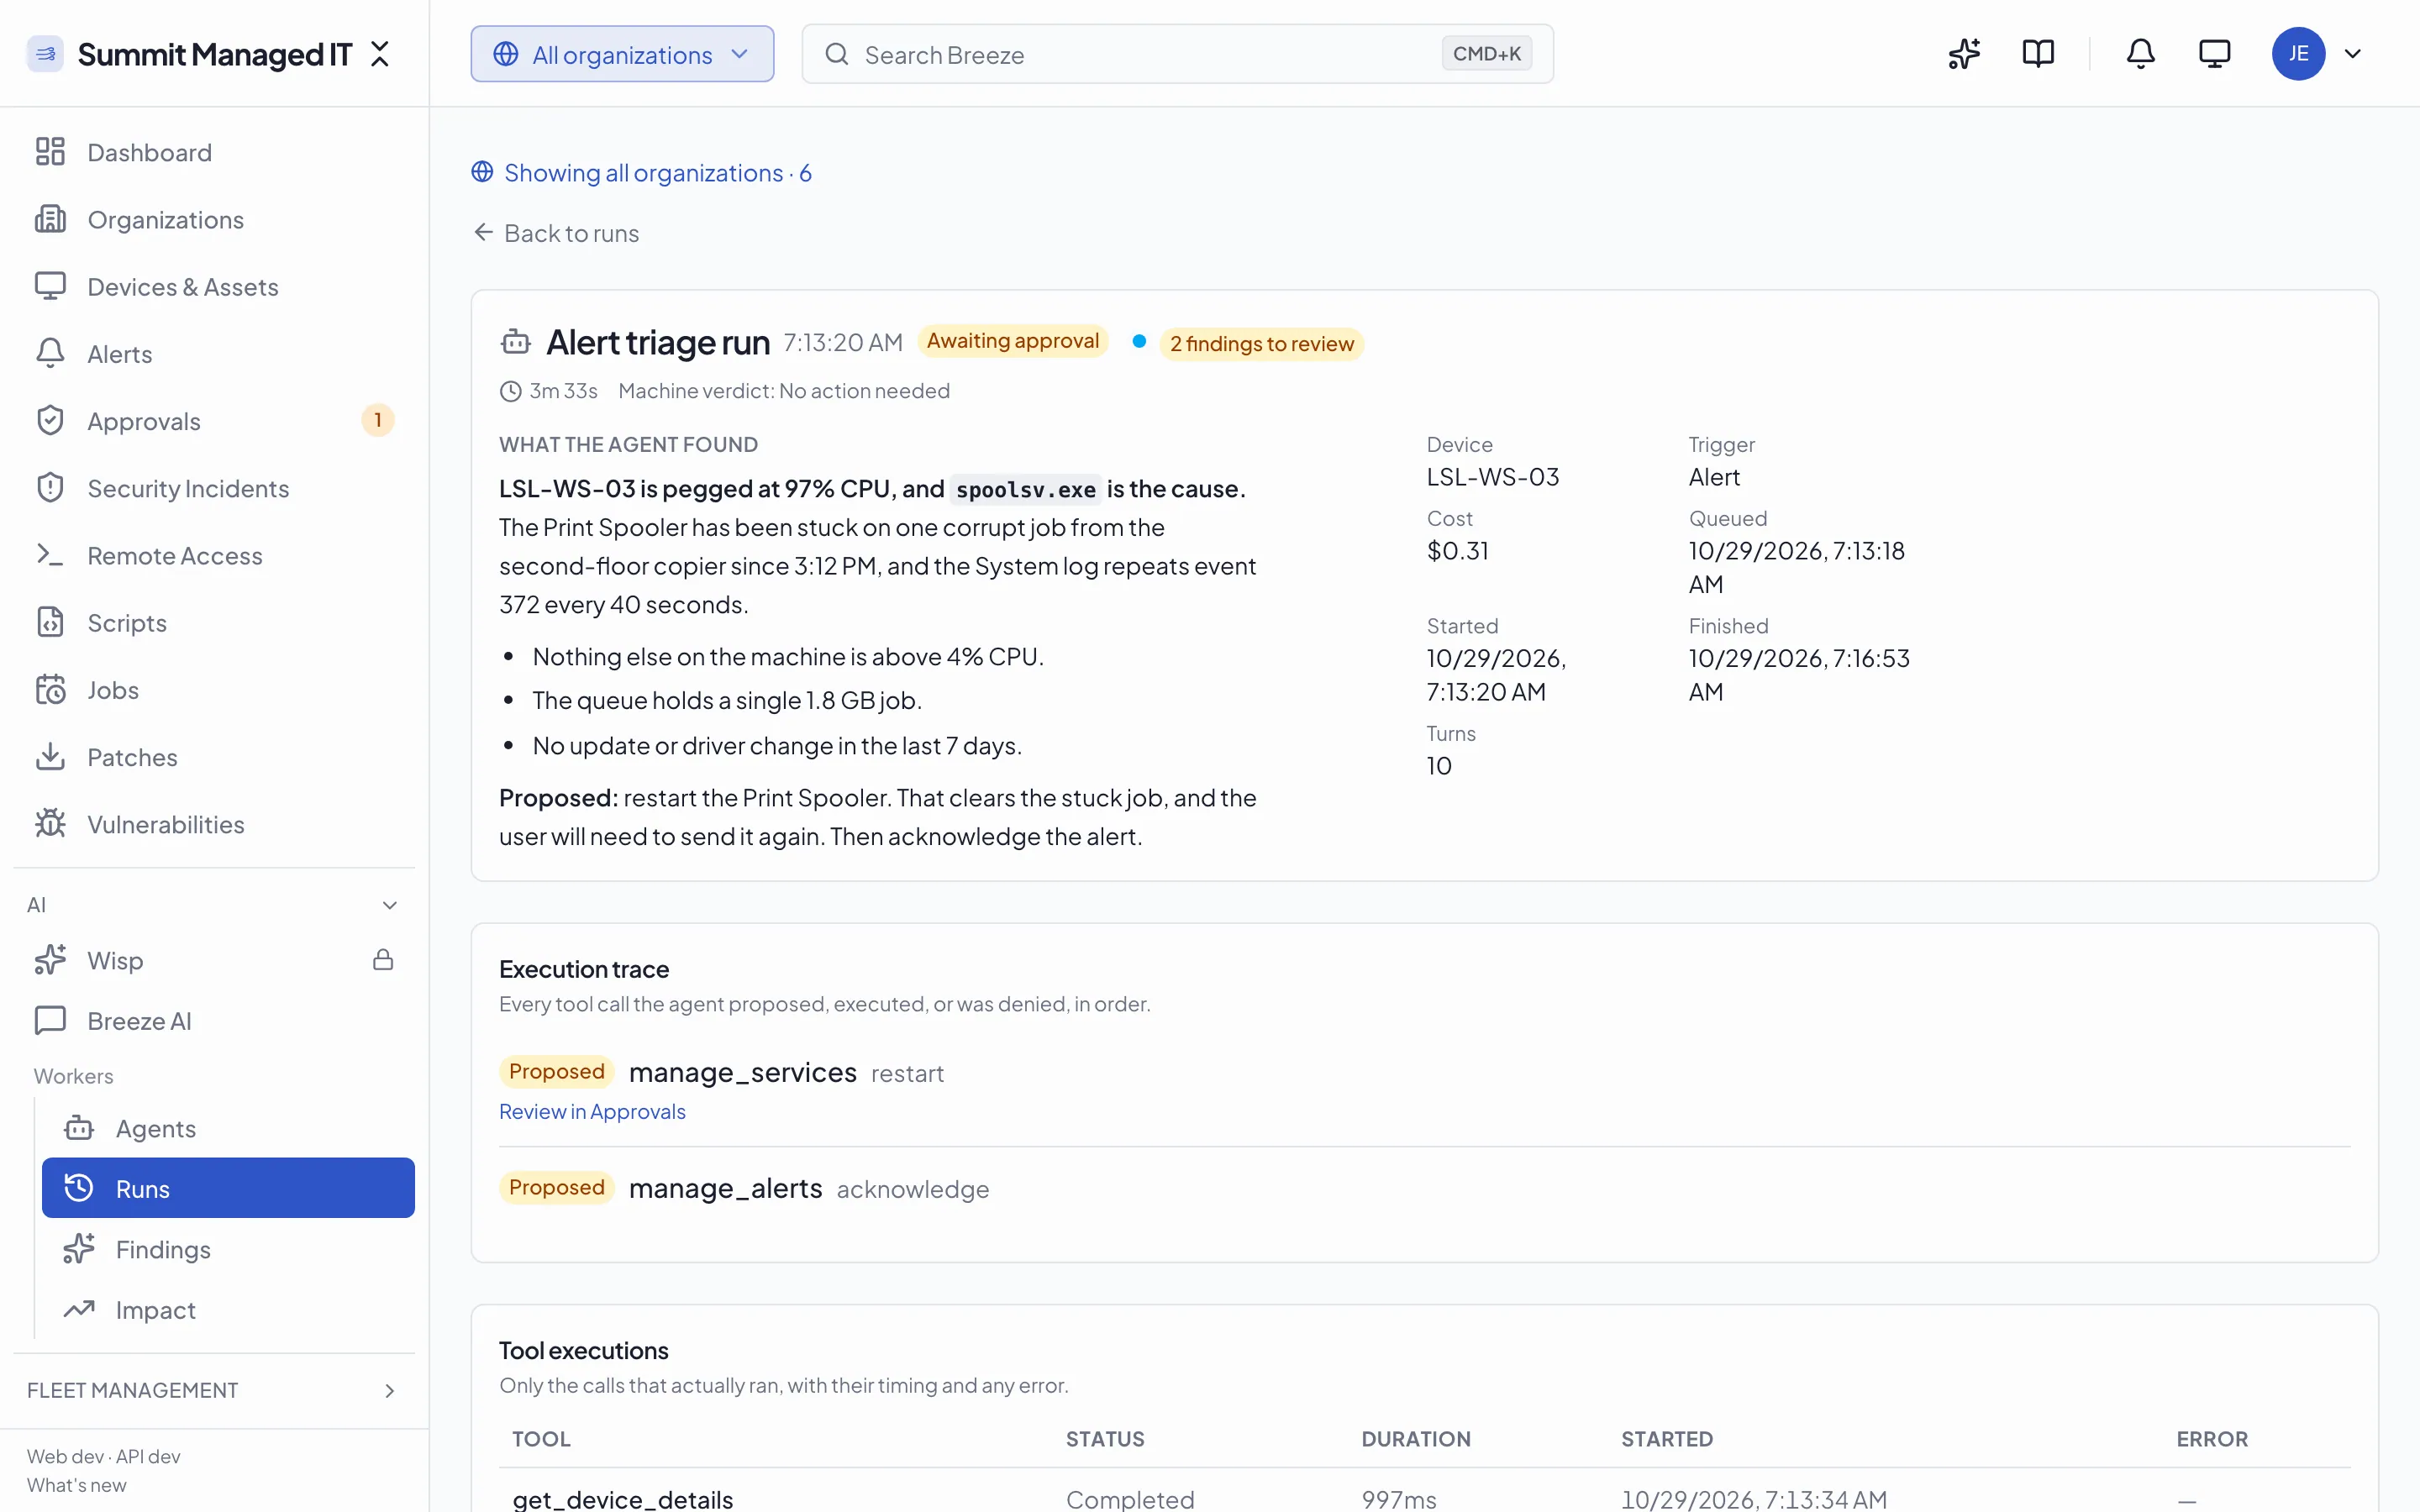
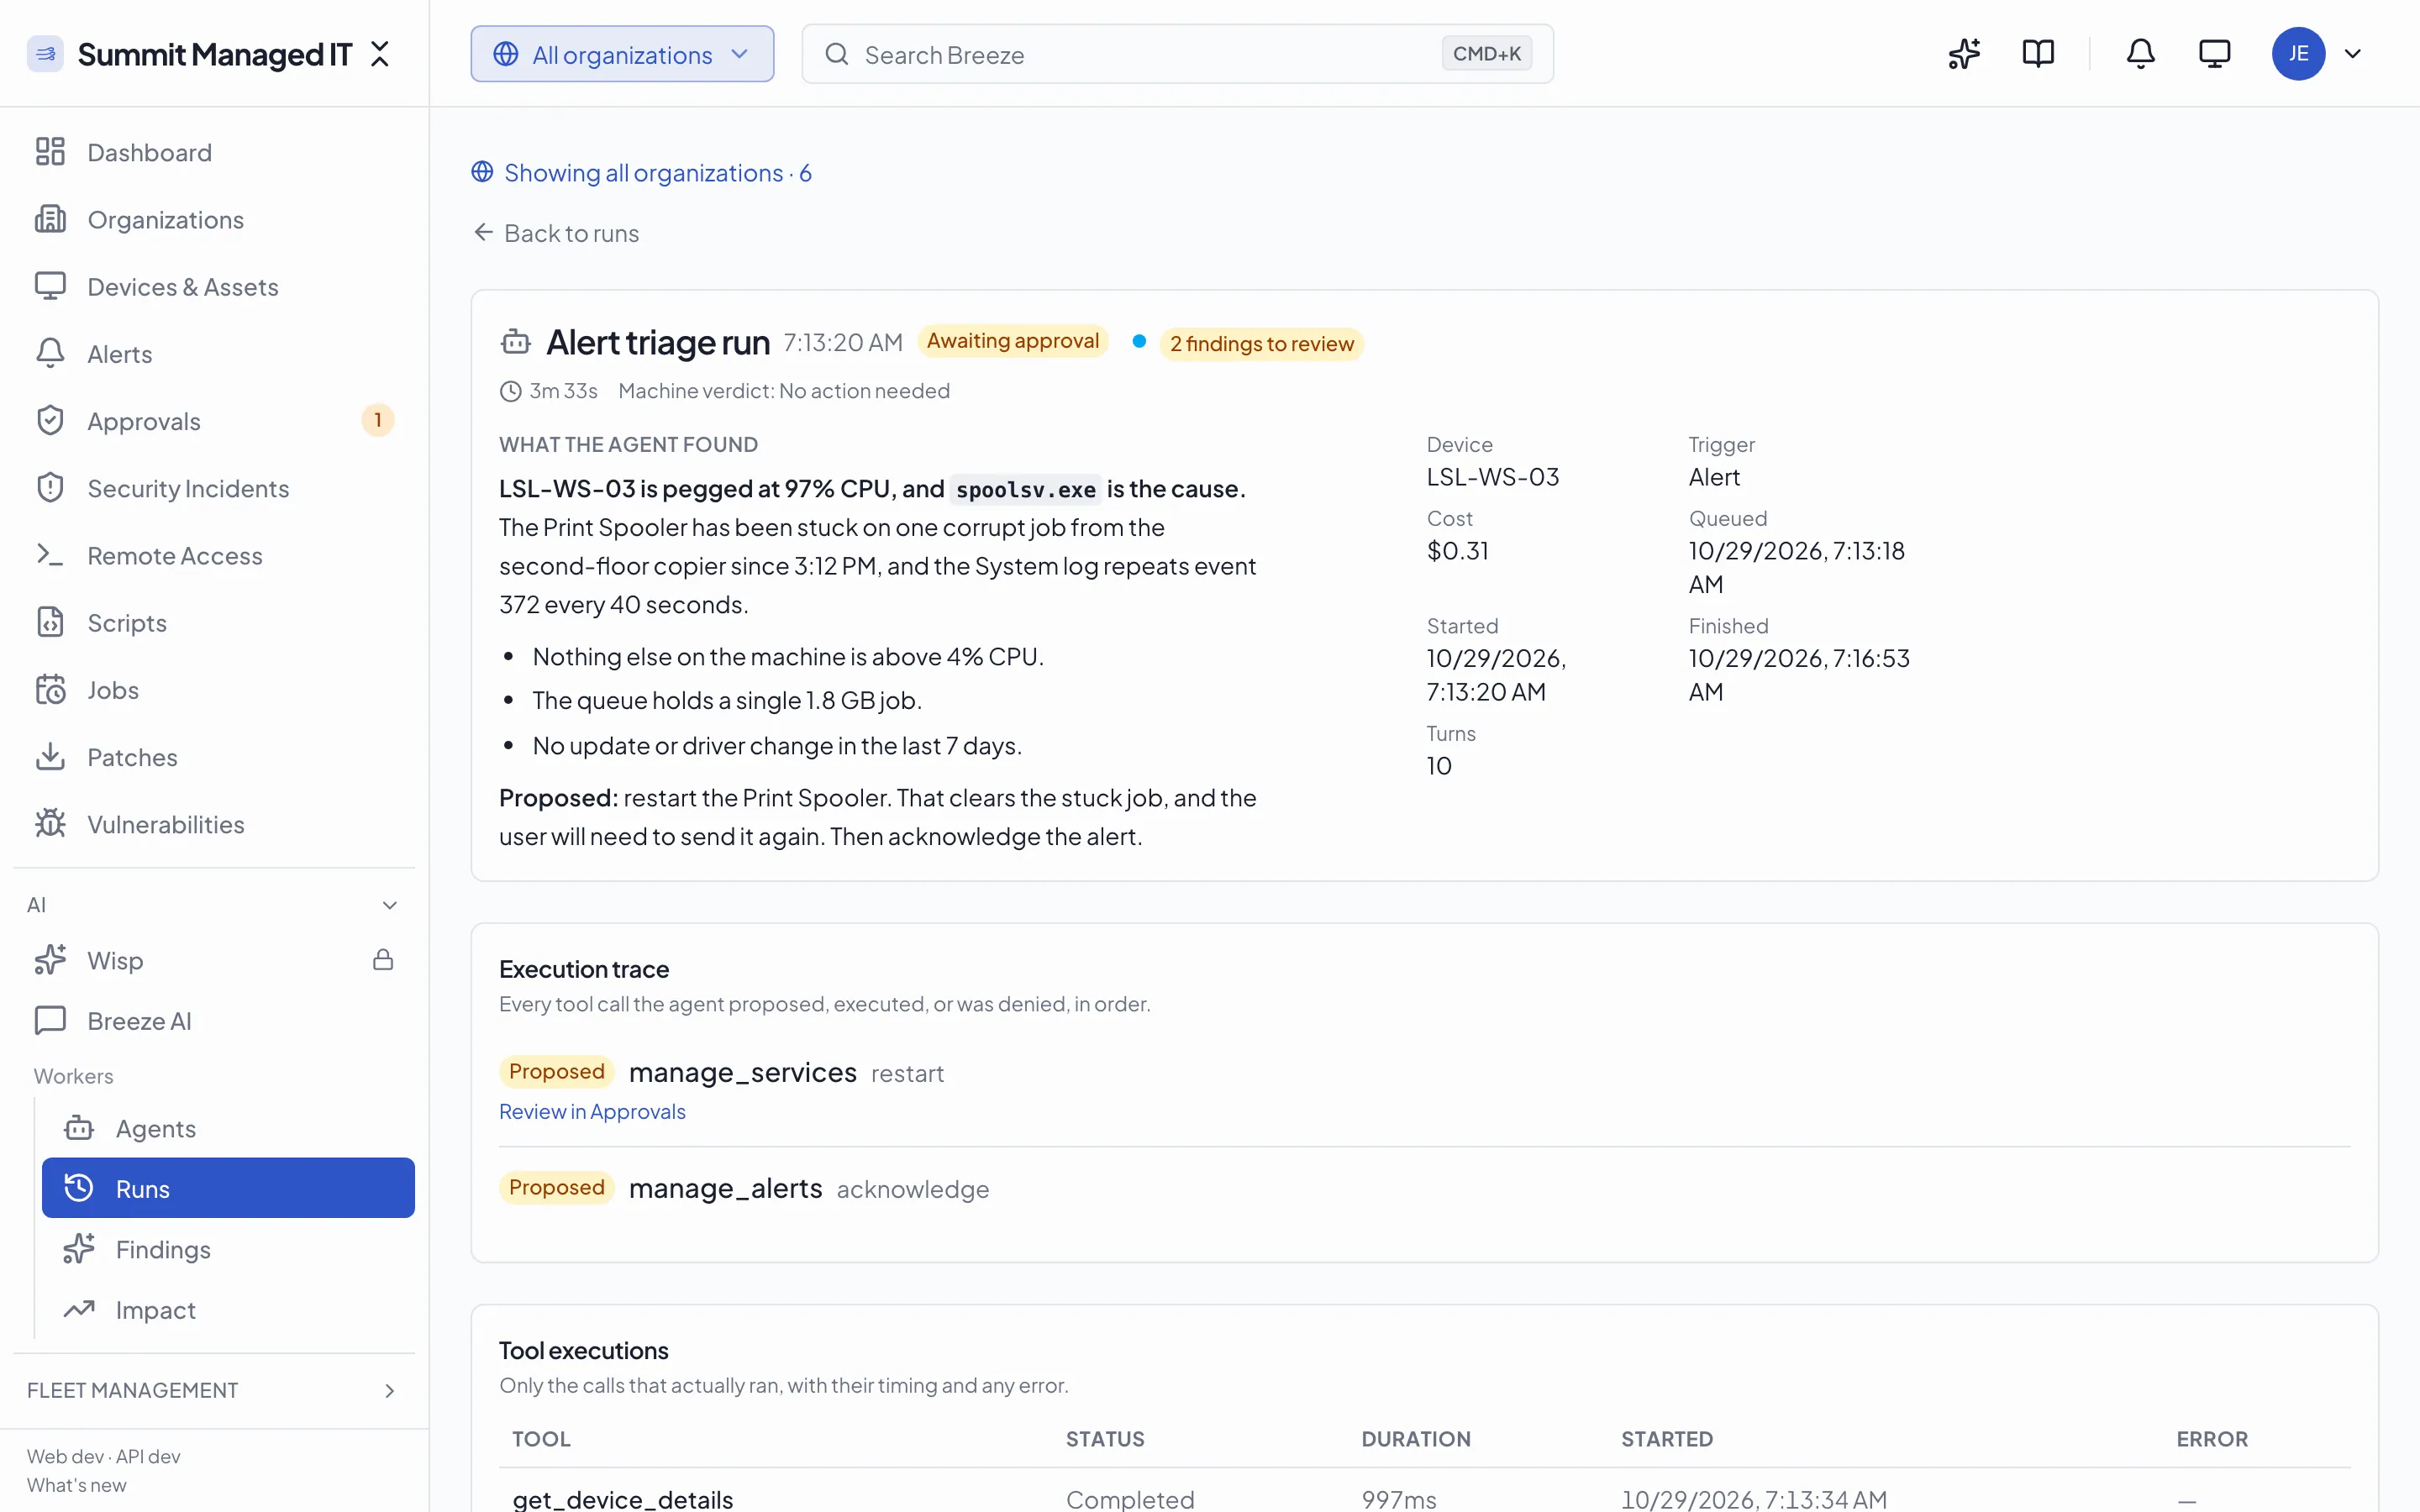
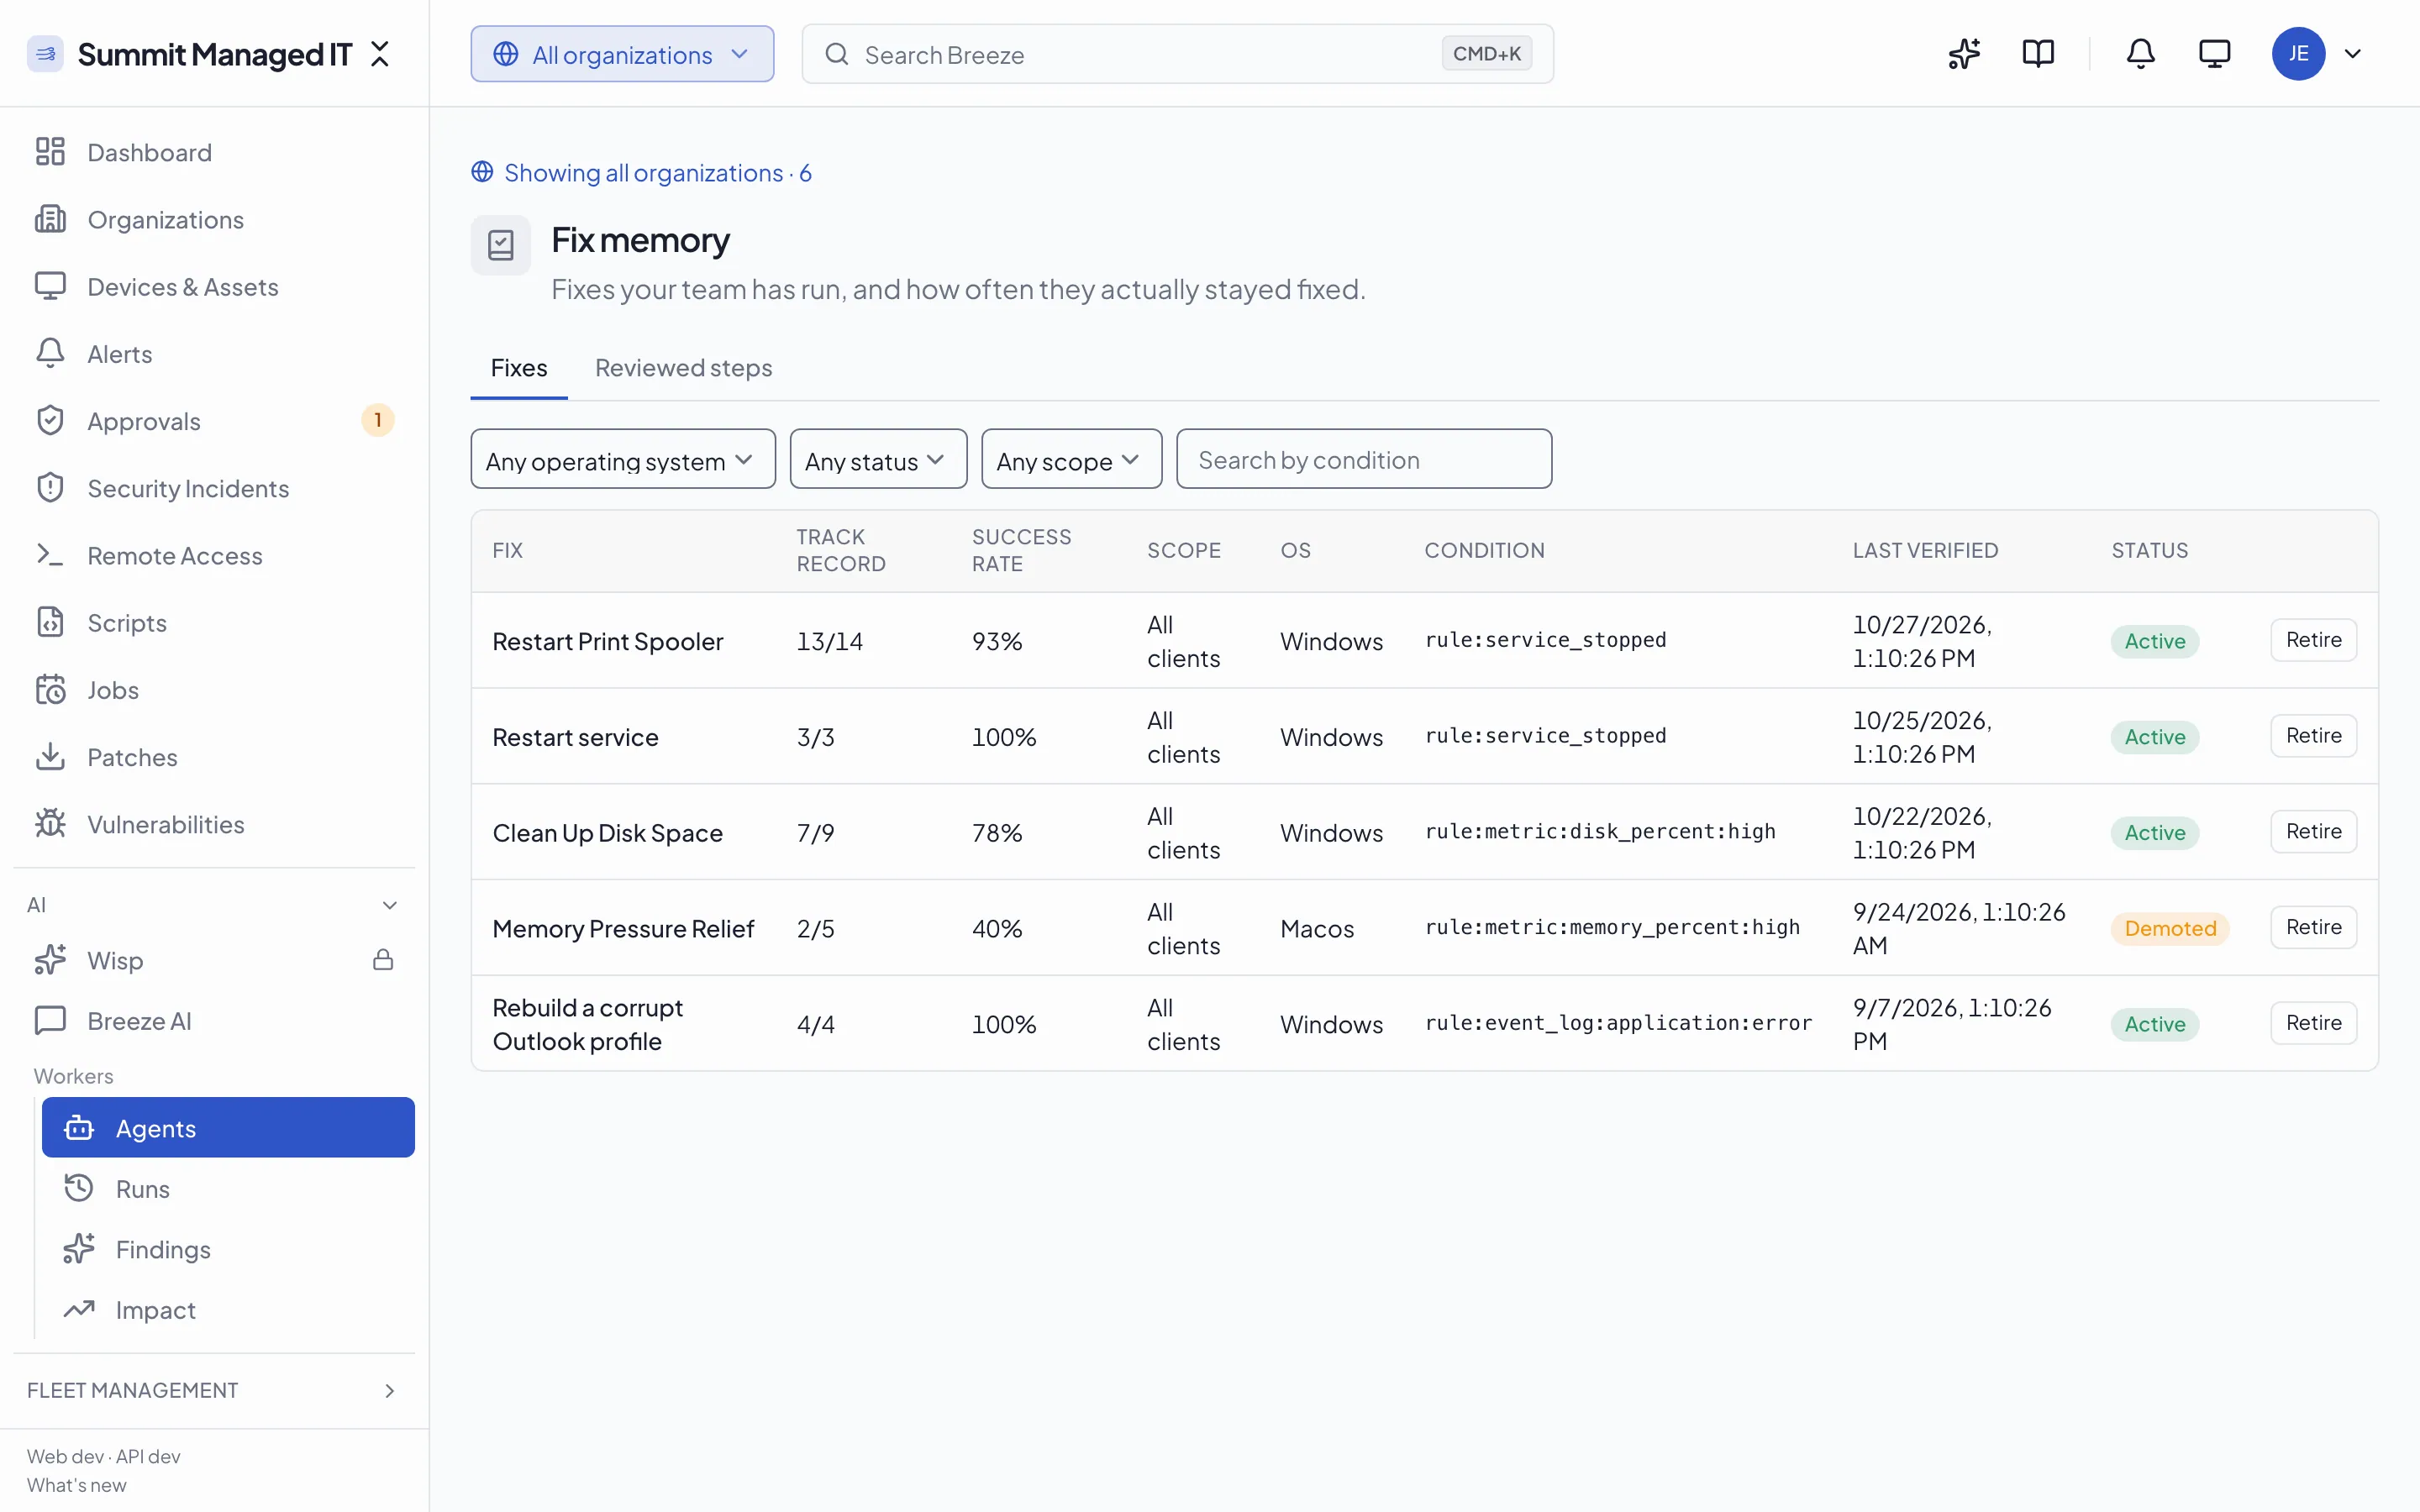
Screenshots from Breeze v0.125.0, captured 2026-10-29, on demo data.
Capabilities
Tiered Action Governance
AI operations are evaluated into Tier 1-4 execution levels with explicit controls over what can run automatically.
Approval Workflow
Tier 3 actions are held for operator approval before execution and tracked in approval history.
Execution Analytics
Risk Engine views expose tool usage, denials, and rate-limit events for operational oversight.
Fleet AI Tools
Fleet-oriented tools cover policies, deployments, patches, automations, alerts, and report generation.
Ready to see The Workers in action?
Start the Cloud Beta in minutes, or deploy for free with Docker Compose. Want a walkthrough first? Book a 20-minute demo.
Ready to try Breeze?
Self-host the open-source agent or join the managed cloud beta. No credit card required.
Related features
All features →AI Risk Engine
Control what AI can do, when, and under whose approval.
AI Computer Control
AI actions with operational guardrails.
First in RMMMCP Server
Let your AI client work the fleet, under the same governance as your team.
Agent Diagnostics
Debug the agent itself, not just the endpoint.
Coming from another RMM? See how Breeze compares on price, features, and openness.
Compare Breeze